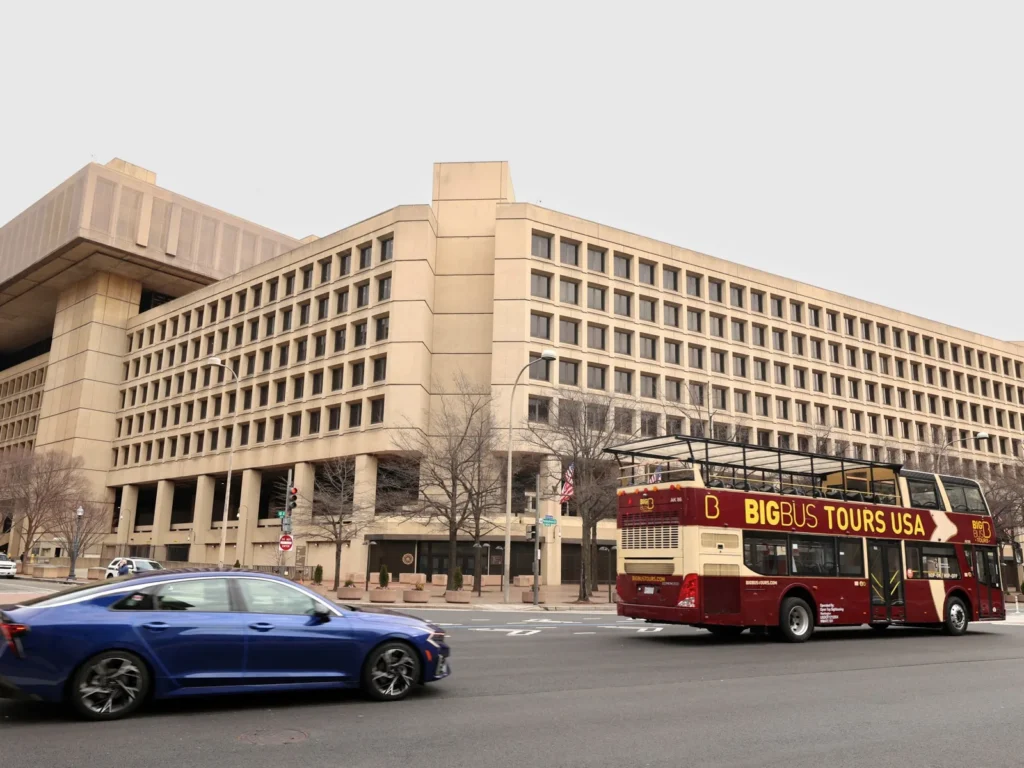
WASHINGTON — The Federal Bureau of Investigation (FBI) said on Wednesday it is investigating a reported breach of its careers website, after a hacking group claimed to have stolen sensitive employee data and internal communications. The agency confirmed the investigation in a statement released to wire services, marking a significant escalation in cybersecurity concerns surrounding federal infrastructure.
The incident centers on the FBI’s official recruitment portal, which the Bureau stated was targeted by unauthorized actors. According to reports from multiple news outlets, a cybercriminal group asserted that it had accessed the site and exfiltrated data belonging to current and former employees. The hackers claimed the stolen information included personal identifiers, contact details, and potentially sensitive operational metadata, though the FBI has not yet publicly confirmed the specific categories of data compromised.
Scope of the Investigation
FBI officials indicated that the investigation is ongoing and involves coordination with the Cybersecurity and Infrastructure Security Agency (CISA) and other federal partners. The Bureau emphasized that it is assessing the extent of the intrusion and the potential impact on national security operations. No immediate threat to ongoing investigations or public safety was reported, but the agency urged employees to remain vigilant against phishing attempts that may exploit the incident.
The timing of the breach has drawn attention from cybersecurity analysts who have long warned about vulnerabilities in federal government digital infrastructure. While the FBI maintains robust security protocols, the successful access to a public-facing recruitment site highlights the persistent challenges posed by advanced persistent threats (APTs) and state-sponsored hacking groups. The investigation is expected to focus on the methods used to bypass security controls and the origin of the attack.
Hacker Claims and Verification
The hacking group responsible for the claim has not been officially identified by the FBI, though its modus operandi and digital footprint are being analyzed by federal cyber units. The group posted details of the alleged breach on a dark web forum, asserting that the data included names, email addresses, and phone numbers of thousands of employees. Independent cybersecurity researchers have begun verifying the authenticity of the leaked data, but no definitive confirmation of the scale or nature of the breach has been provided by the government.
Legal experts noted that the incident may trigger mandatory breach notification requirements under federal law, potentially affecting both current and former staff members. The FBI has not disclosed whether any specific individuals or departments were targeted, nor has it commented on whether the breach was linked to any known foreign adversary.
Broader Cybersecurity Context
This incident adds to a growing list of high-profile cyberattacks on U.S. government agencies in recent years. Previous breaches have targeted the Department of Defense, the Department of Health and Human Services, and the Internal Revenue Service, raising concerns about the resilience of federal digital systems. The FBI’s response underscores the agency’s dual role as both a victim and a primary investigator in the fight against cybercrime.
Congressional lawmakers have called for a review of federal cybersecurity spending and protocols, with some advocating for stricter oversight of third-party vendors that manage government websites. The investigation is expected to continue for several weeks, with updates to be released as new evidence emerges. The FBI has reiterated its commitment to protecting sensitive data and holding those responsible for cyberattacks accountable.
Primary Sources & Official Records
- FBI says investigating breach of ‘very sensitive’ data by hackers
- FBI investigates apparent breach of its jobs website. Hackers claim to have sensitive empl
- FBI investigating hacking group’s claim of massive breach of agent info – NBC News
- FBI investigating hackers’ claim of stolen sensitive employee data, compromised jobs websi